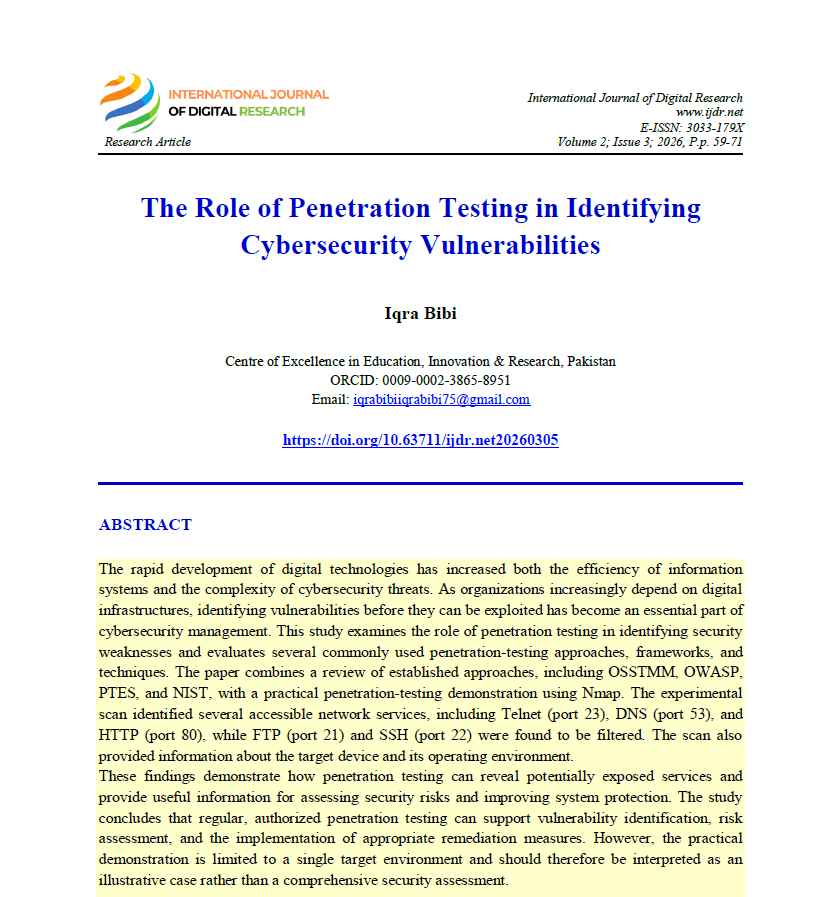
The International Journal of Digital Research (IJDR) has published a new research article examining how penetration testing can contribute to the identification and assessment of cybersecurity vulnerabilities.
The article, “The Role of Penetration Testing in Identifying Cybersecurity Vulnerabilities,” is authored by Iqra Bibi from the Centre of Excellence in Education, Innovation & Research, Pakistan, and appears in Volume 2, Issue 3 (2026) of IJDR.
Cybersecurity threats continue to evolve alongside the growing dependence of organizations on digital infrastructure. Against this background, the study examines penetration testing as a controlled and authorized approach for identifying security weaknesses before they can be exploited. It combines a review of established penetration-testing approaches and frameworks with a practical demonstration using the network-scanning tool Nmap.
From Security Frameworks to Practical Testing
The research discusses several established approaches and frameworks used in penetration testing and security assessment, including OSSTMM, OWASP, PTES, ISSAF, and NIST. It also considers different forms of penetration testing and the principal stages involved in conducting structured security assessments.
A practical component of the study demonstrates the use of Nmap to examine a target system and identify accessible network services. The scan detected open services including Telnet (port 23), DNS (port 53), and HTTP (port 80). The analysis also identified FTP (port 21) and SSH (port 22) as filtered, while operating-system detection provided additional information about the target environment.
Supporting Proactive Cybersecurity
The findings illustrate how penetration testing and network scanning can provide useful information about exposed services, filtered ports, and system environments. Such information can support vulnerability identification, risk assessment, and decisions about appropriate remediation measures.
The study emphasizes the importance of regular and authorized penetration testing as part of broader organizational cybersecurity practices. At the same time, the author notes that the practical demonstration involves a single target environment and should therefore be understood as an illustrative case rather than a comprehensive assessment of penetration-testing effectiveness.
The publication contributes to IJDR’s growing coverage of cybersecurity, penetration testing, vulnerability assessment, and network security.
Read the full article:
https://ijdr.net/volume-2-year-2026/volume-2-issue-3/penetration-testing-cybersecurity-vulnerabilities/
DOI:
https://doi.org/10.63711/ijdr.net20260305
Permanent archive on Zenodo:
https://zenodo.org/records/22304092
How to cite:
Bibi, I. (2026). The Role of Penetration Testing in Identifying Cybersecurity Vulnerabilities. International Journal of Digital Research, 2(3), 59–71. https://doi.org/10.63711/ijdr.net20260305